Trust & Security
Security woven into every tenant environment
Opsia Cloud is engineered for regulated workloads, with defense-in-depth controls, transparent operations, and defined escalation paths.
We combine strong technical safeguards with governance, documentation, and operating practices. Explore how we protect data and help teams work toward compliance goals.
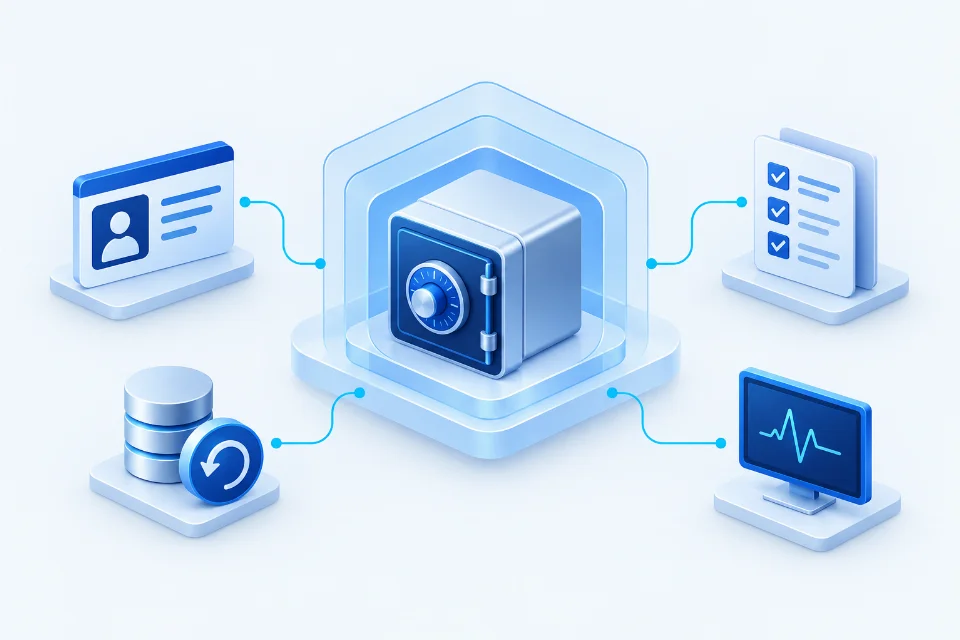
Security pillars
Governance & access
Role-based access, enforced MFA, least-privilege provisioning, and quarterly access reviews.
Platform resilience
Multi-zone architecture, continuous backups, automated failover drills, and site reliability runbooks.
Operational transparency
Real-time telemetry, customer-facing status dashboards, and documented incident communications.
Compliance alignment
Controls can be mapped to SOC 2, ISO 27001, and Canadian regulatory expectations during onboarding and procurement reviews.
Key technical controls
Network segmentation
Dedicated tenant VPCs, private connectivity options, and micro-segmentation enforced by service mesh policies.
Encryption everywhere
TLS 1.3 for data in transit, managed key vaults, and envelope encryption for sensitive secrets.
Managed detection & response
Centralized log analytics, behavioral detection rules, and response workflows supported by our MDR process.
Secure software lifecycle
CI/CD pipelines with automated scanning, peer reviews, and artifact signing before deployment.
Data protection
Immutable backups, configurable retention, and documented data destruction procedures.
Tenant isolation
Logical and optional physical separation with per-tenant IAM boundaries and encryption keys.
Assurance planning
SOC 2 readiness
Control mapping and evidence collection can be scoped for customer and vendor security reviews.
ISO 27001 control planning
ISMS-style policies, risk reviews, and treatment plans can be documented for managed engagements.
Law 25 privacy planning
Quebec privacy expectations can be addressed through privacy impact assessment support, breach-readiness planning, and governance reporting.
Vendor management
Tiered vendor risk assessments, contractual flow-down clauses, and ongoing monitoring.
Looking for more detail?
Request our detailed controls matrix, insurance certificates, or pen-test summary after signing an NDA.
Talk with the Opsia security team
Need to schedule a tabletop exercise, submit a questionnaire, or report a concern? We route requests through defined support and escalation paths.
Operate your SaaS on a trusted Canadian cloud
Join teams that rely on Opsia Cloud for regulated industries, education, public sector, and mission-critical workloads.